
01
Map
Understand identities, trust relationships, privilege, critical workloads and control planes.
Secure the control planes that increasingly define enterprise access and attack paths.
Identify how cloud configuration, identities and entitlements combine to create risk across modern environments.
Tell us the objective, your environment and the decisions you need to make. We will help define a focused engagement.
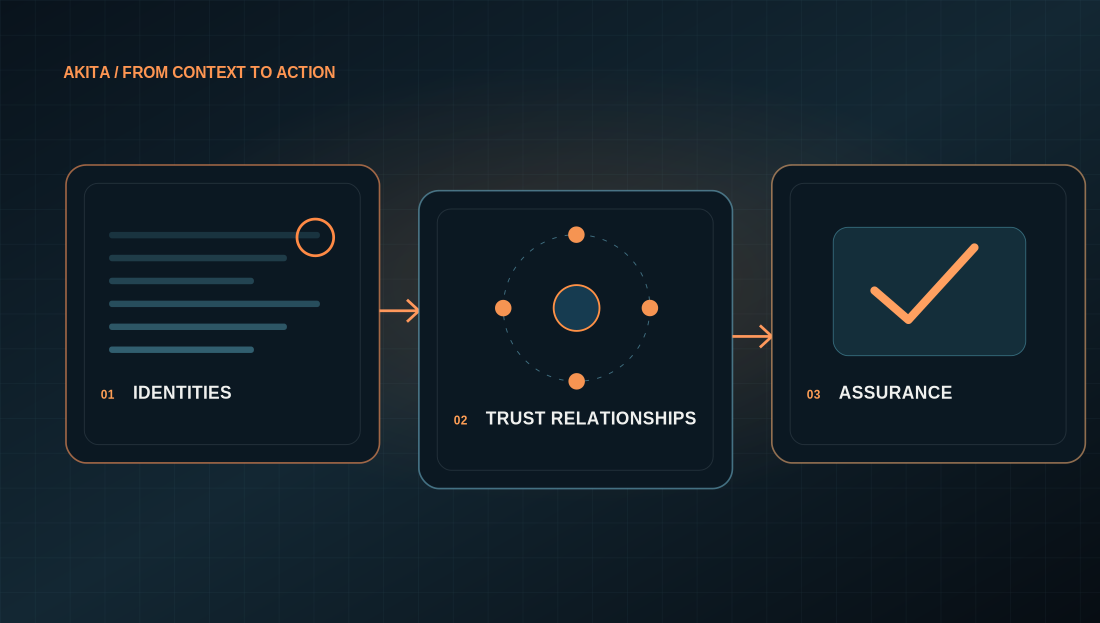 AKITA / TRUST BOUNDARIES MADE VISIBLE
Understand identities, trust relationships, privilege, critical workloads and control planes.
Test realistic paths that could convert configuration weakness into meaningful access.
Prioritise architectural and operational changes that reduce reachable privilege.
Yes. Hybrid identity and trust paths can be included where they affect risk.
It can be either or both. Architecture review and offensive validation are often strongest together.
Yes. Identity-first least privilege and continuous validation are core design themes.
Monitoring in practice
Explore how security monitoring can be designed around detection and accountable response.Already have a cloud and identity security requirement or draft scope? Send it to Akita for a focused scoping conversation.
Request a scope or proposal ↗