
Payment and customer continuity
Define the payment, settlement and customer-service journeys that cannot fail.
Banks, insurers, asset managers and payment organisations need control ownership, resilient critical services and evidence that connects governance to real systems. Akita brings security leadership, engineering and attack validation around that goal.
Banks and payment organisations depend on reliable transaction and customer services. Insurers and asset managers must protect sensitive information and third-party relationships. Relevant duties, including DORA or PCI DSS where applicable, must translate into owned and demonstrable controls.
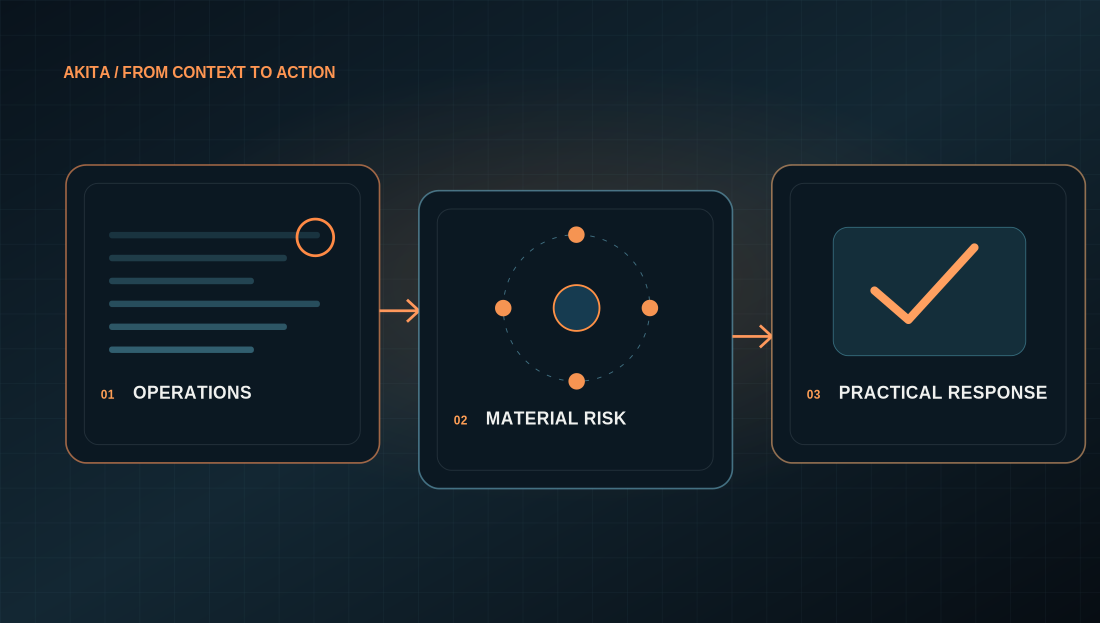 AKITA / SECURITY IN OPERATING CONTEXT
Define the payment, settlement and customer-service journeys that cannot fail.
Examine how digital channels, privileged access and third parties can expose critical services.
Produce evidence, control ownership and a prioritised improvement sequence for risk committees.
Selected organisations in the Akita customer portfolio
Experience relevant to this operating environment

Bring the operational resilience, regulatory assurance or identity question that your financial-services team needs to resolve. We can define a focused scope and the evidence required to support a decision.
Already have a financial services requirement or draft scope? Send it to Akita for a focused scoping conversation.
Request a scope or proposal ↗Akita works across payment, banking and financial-service operating environments. For insurers, asset managers and other regulated organisations, the discussion starts with operational resilience, third-party dependencies, identity and practical security assurance. Applicability of frameworks such as DORA, NIS2 and PCI DSS depends on the organisation and its services.
Explore FinTech security ↗