
01
Align
Establish business priorities, risk appetite, obligations and current security ownership.
Senior security leadership that turns cyber risk into a business-owned plan.
Clarify ownership, turn competing risks into a decision plan, and keep leadership connected to delivery.
Tell us the objective, your environment and the decisions you need to make. We will help define a focused engagement.
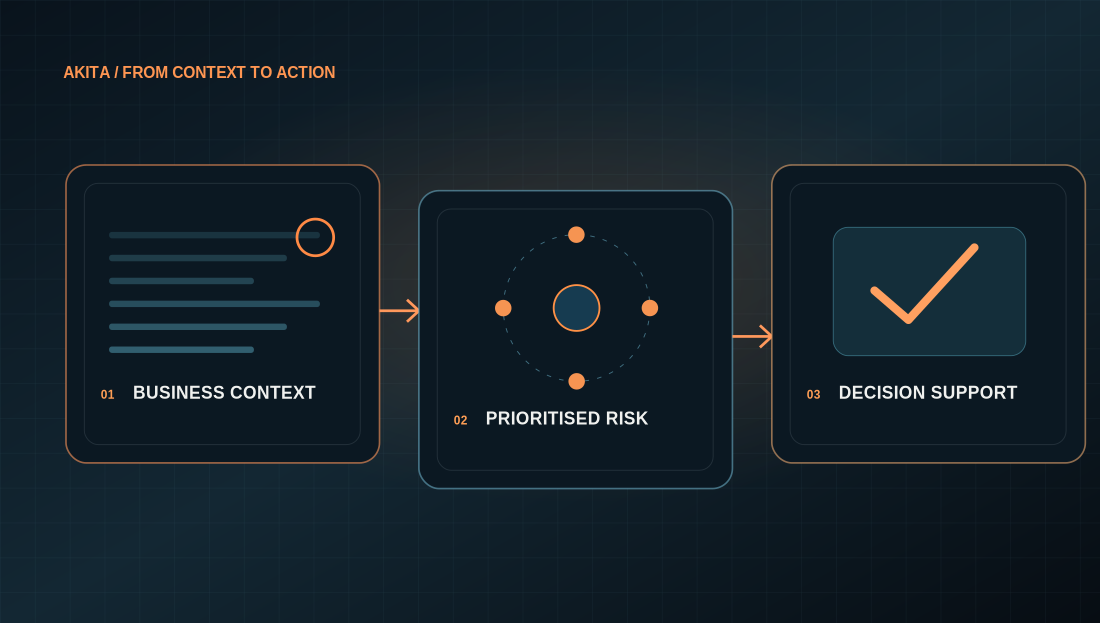 AKITA / DECISIONS THAT CAN BE ACTED ON
Executive clarity, accountable priorities and a security programme built to move from strategy into delivery.
Establish business priorities, risk appetite, obligations and current security ownership.
Turn gaps and dependencies into a sequenced plan with owners and measurable outcomes.
Maintain cadence across leadership, delivery teams, suppliers and assurance activities.
No. The model is designed to lead, extend or structure the capabilities you already have.
Yes. Executive communication and decision support are core parts of the engagement.
Yes. The roadmap can span governance, assurance, architecture and hands-on validation.
Governance in practice
See how regulatory requirements were translated into operational GRC processes.Already have a security leadership requirement or draft scope? Send it to Akita for a focused scoping conversation.
Request a scope or proposal ↗