
01
Map agency
Identify what the model or agent can see, decide, call and change.
Secure AI systems, agents and MCP-style integrations before autonomy turns assumptions into actions.
Examine tool access, instructions, identity, data exposure and control boundaries in AI-enabled workflows.
Tell us the objective, your environment and the decisions you need to make. We will help define a focused engagement.
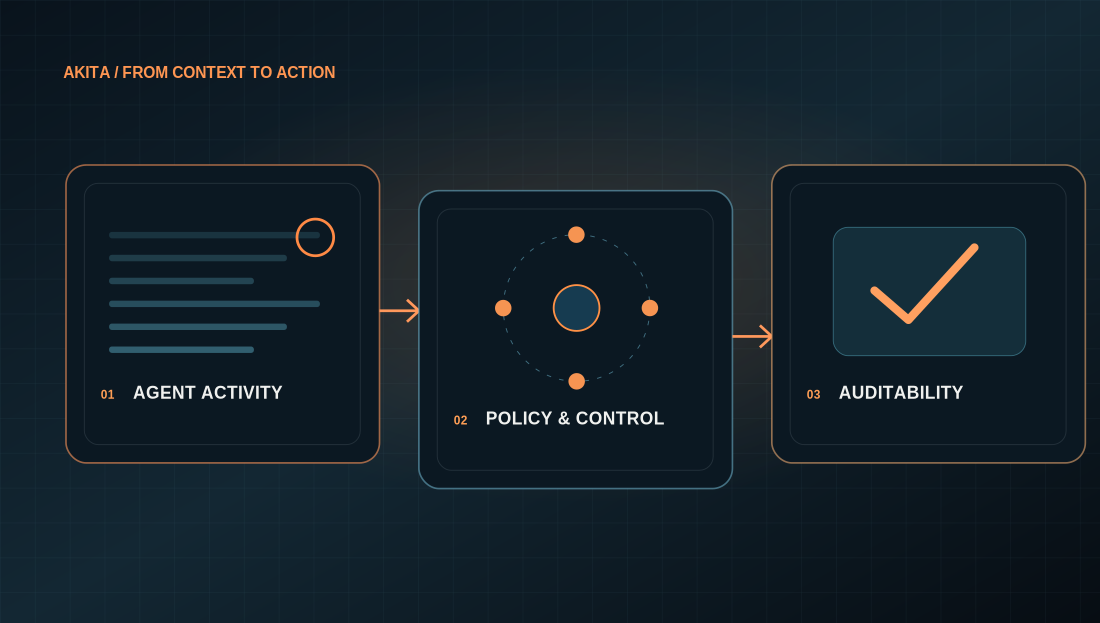 AKITA / AGENCY UNDER CONTROL
Identify what the model or agent can see, decide, call and change.
Test misuse paths across prompts, tools, identities, data and connected systems.
Design least-agency permissions, approval points, telemetry and containment.
Yes, where relevant, but the scope also covers the surrounding tools, identities, data and action paths.
The system can take actions, so permissions, tool boundaries and oversight matter as much as model behaviour.
Yes. Connector trust, tool exposure, identity, secrets and allowed actions can all be assessed.
Validation in practice
Explore how attack-path testing can focus remediation on the risks that matter.Already have an AI security requirement or draft scope? Send it to Akita for a focused scoping conversation.
Request a scope or proposal ↗