
01
Understand
Map business purpose, data, users, integrations, trust boundaries and constraints.
Translate business change into security designs that teams can implement and defend.
Review trust boundaries, identity, segmentation and architecture choices before weaknesses become costly dependencies.
Tell us the objective, your environment and the decisions you need to make. We will help define a focused engagement.
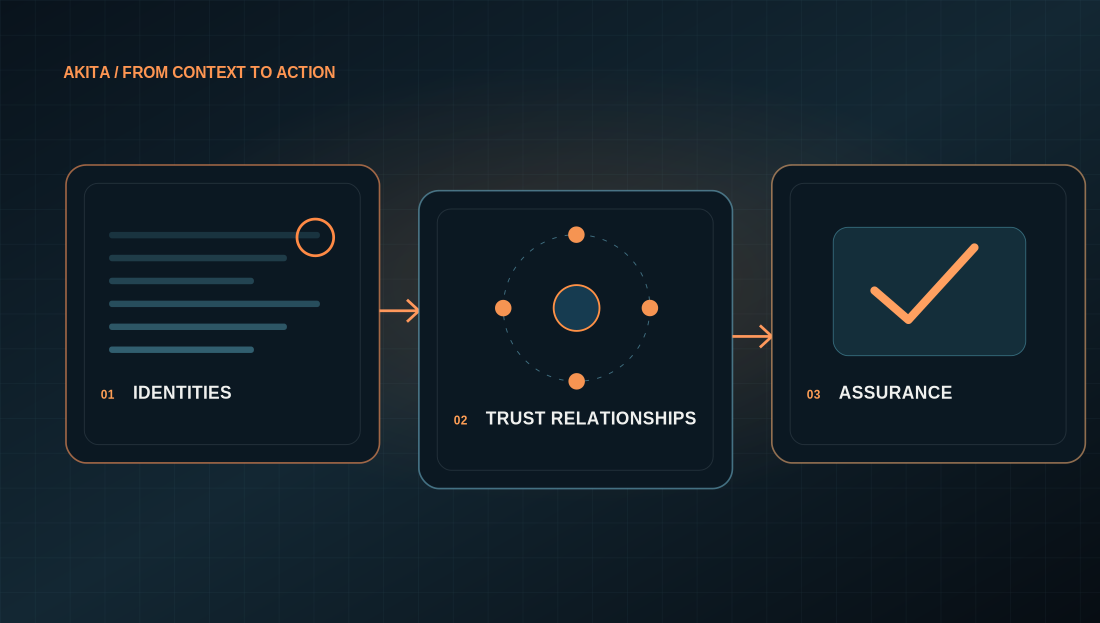 AKITA / TRUST BOUNDARIES MADE VISIBLE
Map business purpose, data, users, integrations, trust boundaries and constraints.
Create practical security requirements and control patterns for the target architecture.
Review implementation decisions, exceptions and evidence against agreed acceptance criteria.
Yes. We can review a design at any stage and focus on the decisions that still can be influenced.
Yes. Deliverables can include requirements, diagrams, decision records and acceptance criteria.
Yes. The method applies across enterprise, cloud, SaaS and application architectures.
Monitoring in practice
Explore how security monitoring can be designed around detection and accountable response.Already have a defined requirement? Share the context and we will agree a focused scoping conversation.
Request a scope or proposal ↗