
01
Select
Choose meaningful attacker techniques and control assumptions to validate.
Collaborative attack-and-defend validation that improves detection, response and control performance.
Use collaborative exercises to see what defenders observe, where investigation stalls and which controls need tuning.
Tell us the objective, your environment and the decisions you need to make. We will help define a focused engagement.
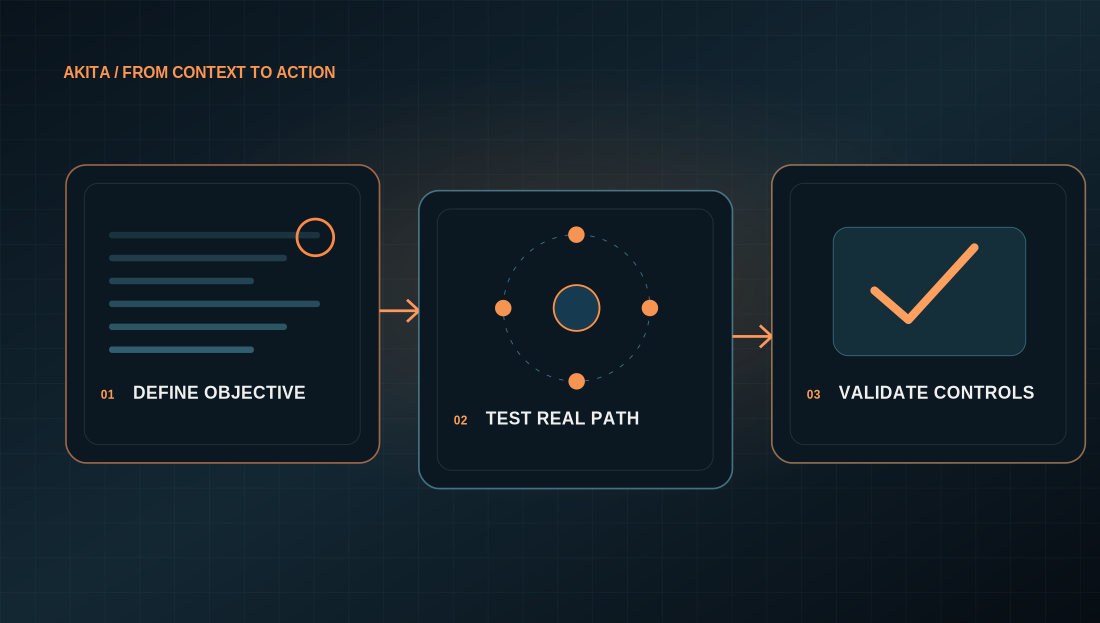 AKITA / TESTED, NOT ASSUMED
Choose meaningful attacker techniques and control assumptions to validate.
Run the technique, inspect visibility and follow the operational response path.
Tune detections, controls and workflows, then repeat until the expected outcome is observable.
Security operations, engineering, infrastructure, cloud and application owners may all be relevant depending on scope.
No. Purple Team can also help organisations establish what useful detection and response should look like.
Yes. The output connects tested techniques to visibility, ownership and remediation actions.
Validation in practice
Explore how attack-path testing can focus remediation on the risks that matter.Already have a defined requirement? Share the context and we will agree a focused scoping conversation.
Request a scope or proposal ↗