
01
Scope
Define assets, attack surface, constraints and the decisions the test must support.
Real-world testing across applications, APIs, infrastructure and cloud environments.
Test the assets and trust boundaries that matter to the business, then move from findings to prioritised action.
Tell us the objective, your environment and the decisions you need to make. We will help define a focused engagement.
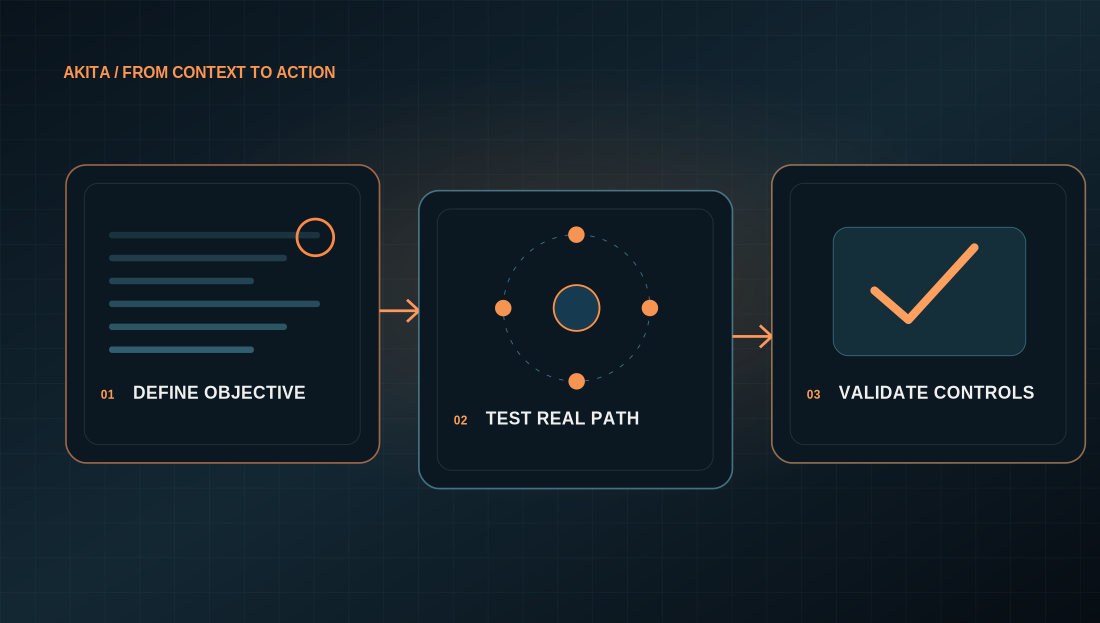 AKITA / TESTED, NOT ASSUMED
Define assets, attack surface, constraints and the decisions the test must support.
Combine manual testing, tooling and attacker thinking to validate exploitable paths.
Prioritise findings by realistic impact and provide evidence teams can reproduce.
Yes. Engagements can include REST, GraphQL, SPAs, authentication flows and supporting infrastructure.
Retesting can be included so teams can verify that remediation closes the original attack path.
Technical severity is combined with exploitability, exposure and business context.
Validation in practice
Explore how attack-path testing can focus remediation on the risks that matter.Already have a penetration testing requirement or draft scope? Send it to Akita for a focused scoping conversation.
Request a scope or proposal ↗Need recurring adversarial testing and verification beyond a point-in-time assessment?
Explore Continuous Red Teaming ↗