
01
Understand
Map the business context, critical assets, current controls and constraints.
Turn technical exposure into decisions the board can understand, own and revisit.
Connect exposure, regulatory duties and business consequences into a conversation the leadership team can use.
Tell us the objective, your environment and the decisions you need to make. We will help define a focused engagement.
We help organisations establish a decision-ready view of cyber risk: what matters to the business, which scenarios could materially disrupt it, how current controls change those scenarios and which choices need executive ownership.
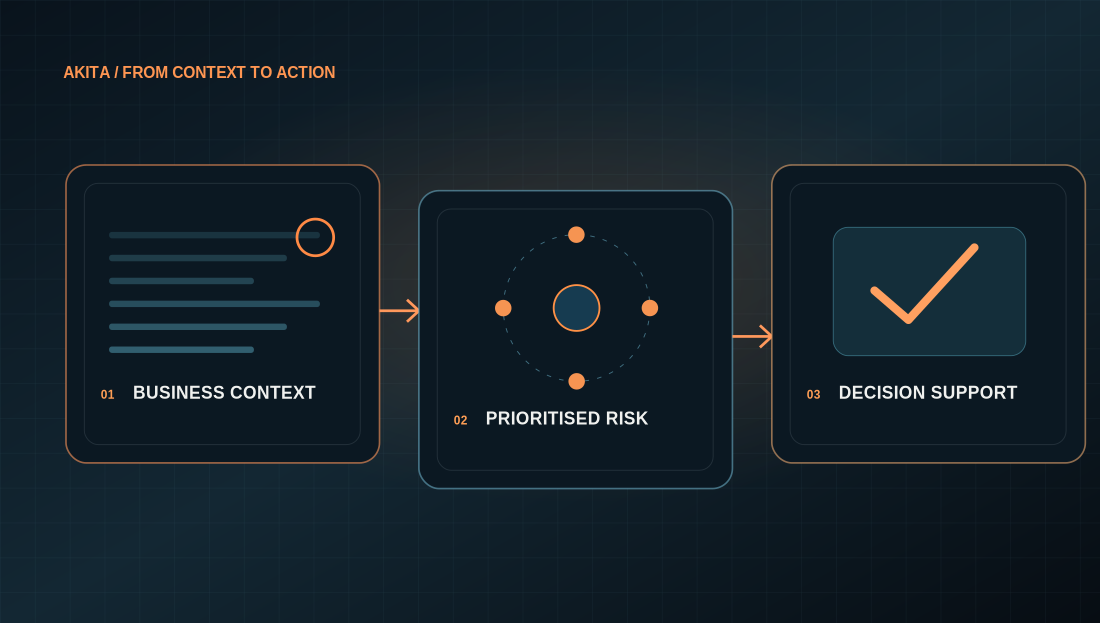 AKITA / DECISIONS THAT CAN BE ACTED ON
Map the business context, critical assets, current controls and constraints.
Test the assumptions that matter using architecture review, evidence and adversarial techniques.
Translate evidence into priorities, owners, implementation work and measurable retest.
We begin with the business outcome, current state and the assumptions that need validation.
Yes. Solutions deliberately combine the capabilities required by the problem.
The structure is defined, while scope and sequence are tailored to the environment.
Governance in practice
See how regulatory requirements were translated into operational GRC processes.Whether you need security leadership, adversarial testing or a clearer view of risk, start with the problem as it exists today.