
01
Map
Identify obligations, scope, stakeholders, controls and existing evidence.
Governance and compliance that produce operational clarity, not paperwork for its own sake.
Translate obligations into controls, responsibilities and evidence that reflect how the organisation actually operates.
Tell us the objective, your environment and the decisions you need to make. We will help define a focused engagement.
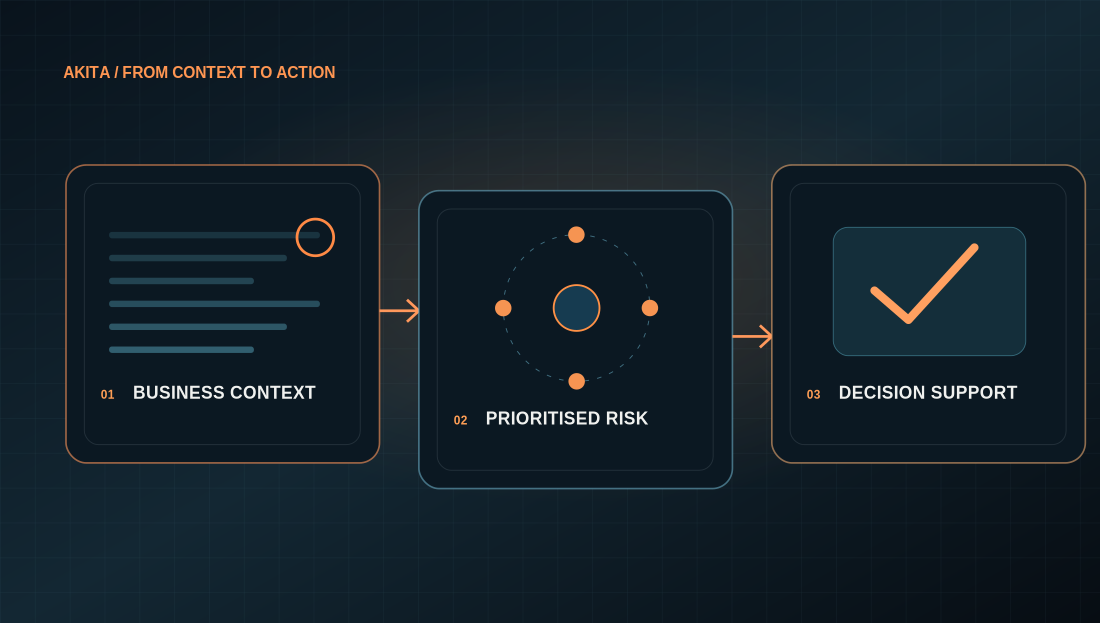 AKITA / DECISIONS THAT CAN BE ACTED ON
Identify obligations, scope, stakeholders, controls and existing evidence.
Create a workable control set, ownership model and remediation plan.
Operationalise recurring evidence, review cadence and audit readiness.
Depending on engagement scope and applicability, advisory work can address ISO 27001, GDPR-related security obligations, DORA, NIS2, PCI DSS, SOC 2 readiness, Cyber Essentials and Israeli privacy requirements. We distinguish readiness support from formal certification or independent assurance.
Read the GRC guide ↗Yes. We can assess gaps, structure controls and evidence, and support remediation toward readiness.
Yes. Scope can include vendor classification, due diligence, contractual expectations and remediation tracking.
Yes. Technical validation can provide direct evidence that selected controls work in practice.
Governance in practice
See how regulatory requirements were translated into operational GRC processes.Already have a GRC requirement or draft scope? Send it to Akita for a focused scoping conversation.
Request a scope or proposal ↗