
01
Understand
Map the business context, critical assets, current controls and constraints.
Test the assumptions that decide whether ransomware becomes disruption or catastrophe.
Examine protective controls, response dependencies and recovery assumptions across the systems the business relies on.
Tell us the objective, your environment and the decisions you need to make. We will help define a focused engagement.
Ransomware resilience depends on more than backups. We examine identity, privilege, segmentation, detection, recovery assumptions and response workflows, then validate the paths that could allow an attacker to spread or block recovery.
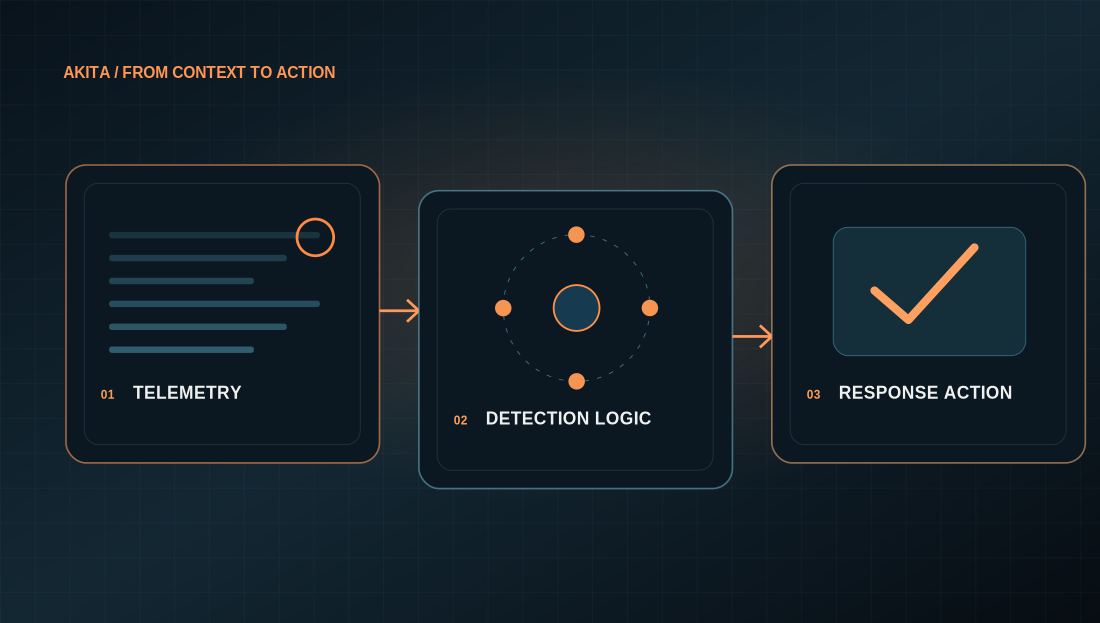 AKITA / A CLEARER SIGNAL
Map the business context, critical assets, current controls and constraints.
Test the assumptions that matter using architecture review, evidence and adversarial techniques.
Translate evidence into priorities, owners, implementation work and measurable retest.
We begin with the business outcome, current state and the assumptions that need validation.
Yes. Solutions deliberately combine the capabilities required by the problem.
The structure is defined, while scope and sequence are tailored to the environment.
Validation in practice
Explore how attack-path testing can focus remediation on the risks that matter.Already have a defined requirement? Share the context and we will agree a focused scoping conversation.
Request a scope or proposal ↗