
01
Understand
Map the business context, critical assets, current controls and constraints.
Put boundaries around what autonomous systems can see, call and change.
Bring security engineering to MCP interfaces, tool invocation, credential handling and operational oversight.
Tell us the objective, your environment and the decisions you need to make. We will help define a focused engagement.
We assess agentic AI architectures as connected security systems rather than isolated models. That means reviewing model behaviour together with identities, tool permissions, MCP-style connectors, secrets, data flows, approval gates, logging and containment.
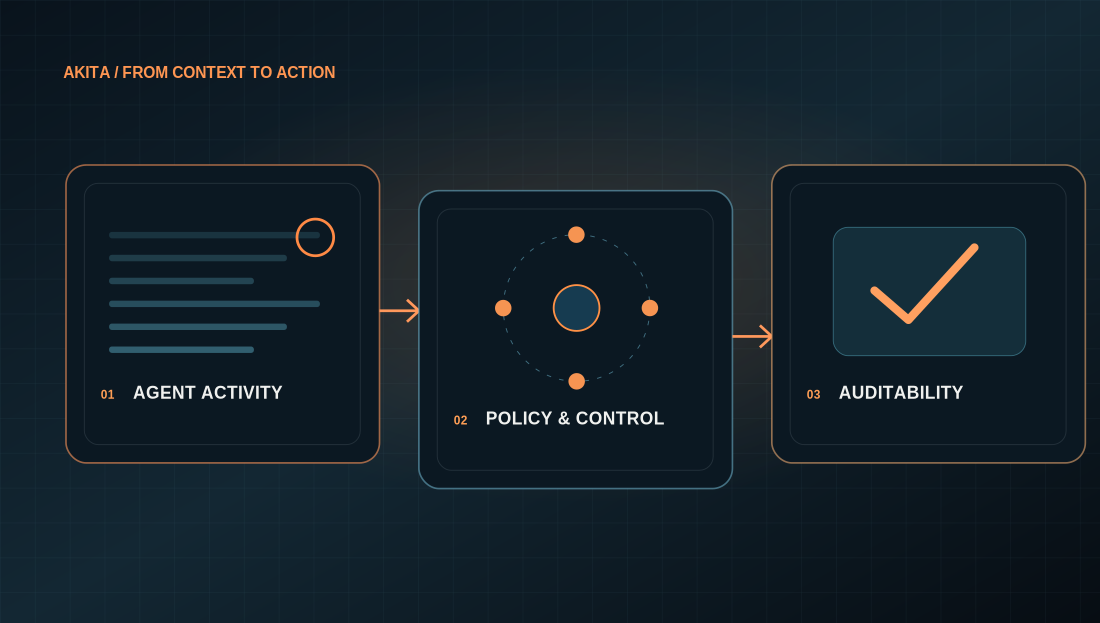 AKITA / AGENCY UNDER CONTROL
Map the business context, critical assets, current controls and constraints.
Test the assumptions that matter using architecture review, evidence and adversarial techniques.
Translate evidence into priorities, owners, implementation work and measurable retest.
We begin with the business outcome, current state and the assumptions that need validation.
Yes. Solutions deliberately combine the capabilities required by the problem.
The structure is defined, while scope and sequence are tailored to the environment.
Validation in practice
Explore how attack-path testing can focus remediation on the risks that matter.Whether you need security leadership, adversarial testing or a clearer view of risk, start with the problem as it exists today.